
Why Telemedicine’s Geographic Flexibility Is a Legal Double‑Edged Sword
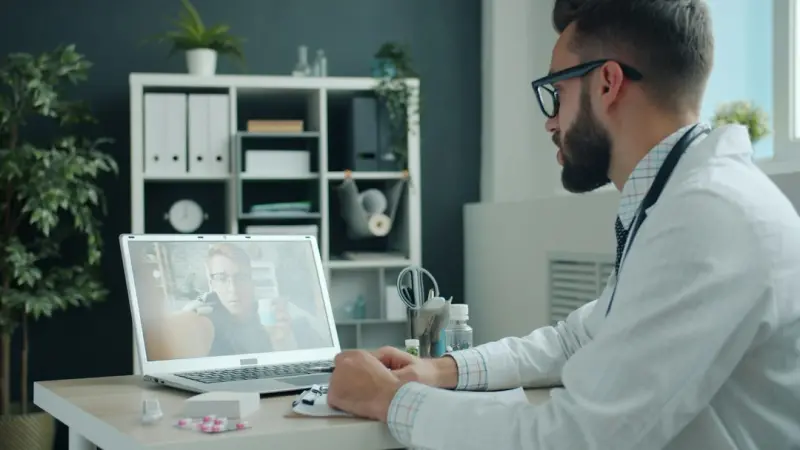
When I first stepped into a virtual consultation room, I was struck by the sheer convenience: a patient in a rural town, a specialist in a metropolitan hub, and a seamless video link that made distance irrelevant. Yet, as a lawyer who spends her days parsing the fine print of health regulations, I quickly realized that every click, every pixel of that screen carries a cascade of legal implications. The promise of telemedicine—borderless access, reduced overhead, and real‑time care—collides with a patchwork of state licensure rules, data‑privacy statutes, and emerging technology concerns. In this post, I’ll walk you through the most pressing legal challenges and practical steps for providers who want to scale their virtual services without stepping into a regulatory minefield.
The State Licensure Maze: No More “One License Fits All”
In the United States, the practice of medicine remains a state‑regulated activity. Each state maintains its own medical board, its own standards for licensure, and its own disciplinary processes. For a telehealth practice that serves patients across state lines, this means you can’t simply rely on a single license. The gig‑platform era taught us that “work” can be geographically fluid, but medical law stubbornly clings to geography.
Key takeaways:
- Dual or Multistate Licensure: Many physicians obtain licenses in multiple states, but this approach quickly becomes cost‑prohibitive as the number of states grows.
- Interstate Compacts: The Interstate Medical Licensure Compact (IMLC) offers a streamlined pathway for qualified physicians to obtain licensure in participating states. However, only 30+ states currently participate, and the compact does not cover all specialties.
- Telehealth‑Specific Exceptions: Some states have “temporary” telehealth provisions that allow out‑of‑state providers to treat patients for a limited period, often tied to emergency declarations or specific disease outbreaks.
Before you schedule your next cross‑state consult, run a licensure audit. Map every state you intend to serve, verify its participation in the IMLC, and check for any telehealth‑specific carve‑outs. This upfront diligence can save you from costly disciplinary actions down the line.
Data Privacy: HIPAA Meets State‑Specific Rules
Telemedicine platforms sit at the intersection of the Health Insurance Portability and Accountability Act (HIPAA) and a growing chorus of state privacy statutes—California’s CCPA, Virginia’s CDPA, Colorado’s CPA, and the emerging “Medical Data Privacy Act” proposals in several states. While HIPAA establishes a federal baseline for protected health information (PHI), it does not preempt stricter state laws.
What does this mean for your virtual practice?
- Encryption and Transmission Security: End‑to‑end encryption is non‑negotiable. Yet, some state statutes require “reasonable” security measures beyond encryption, such as regular penetration testing and documented breach response plans.
- Patient Consent: HIPAA allows for implied consent in treatment contexts, but many states now mandate explicit, written consent for remote data collection, especially when biometric data (e.g., heart‑rate monitors) is transmitted.
- Data Residency: A handful of states are considering legislation that would require health data to be stored on servers physically located within the state. If your cloud provider’s data centers are overseas, you could be non‑compliant without even realizing it.
To stay compliant, adopt a “privacy‑by‑design” approach: work with a cloud vendor that can guarantee data residency options, embed robust consent workflows into your platform, and maintain a documented risk assessment that reflects both HIPAA and any applicable state statutes.
AI‑Driven Diagnostics: The Patent and Liability Crossroads
Artificial intelligence is reshaping diagnostic workflows—from radiology algorithms that flag suspicious nodules to predictive analytics that stratify patients for chronic disease management. While the clinical benefits are undeniable, the legal landscape surrounding AI‑generated medical insights is still forming. In particular, the intersection of AI‑driven diagnostic software patents and malpractice liability is a hot topic.
Two legal fronts demand attention:
- Intellectual Property Ownership: If you develop an AI tool in-house, who owns the patent? The answer often hinges on employment contracts and the presence of “invention assignment” clauses. In many SaaS‑oriented environments, the employer claims ownership, but clinicians who contribute domain expertise may have a claim to joint inventorship.
- Standard of Care and Algorithmic Transparency: Courts are beginning to ask whether reliance on a “black‑box” AI meets the standard of care. If an algorithm misclassifies an image, is the physician liable, the algorithm developer, or both? Some jurisdictions are leaning toward “shared liability” models, especially when the provider cannot reasonably explain the algorithm’s decision‑making process.
Practical steps:
- Document every instance where an AI recommendation informs clinical judgment. Include the algorithm version, confidence score, and any human overrides.
- Negotiate clear IP clauses with any third‑party AI vendors, ensuring you retain the right to audit and modify the underlying code if needed.
- Educate clinicians on the limits of AI outputs and embed “explainability” features into your platform whenever possible.
Algorithmic Bias and the Risk of Discriminatory Care
Even the most well‑intentioned AI models can inherit biases from the data they were trained on. When these tools are deployed in telemedicine, the risk of inadvertently providing sub‑par care to certain demographic groups escalates. The legal implications of such bias were highlighted in a recent discussion on algorithmic bias in clinical decision tools, where plaintiffs have begun suing for disparate impact under both state anti‑discrimination statutes and the federal Civil Rights Act.
Key legal considerations:
- Disparate Treatment vs. Disparate Impact: Even if a provider does not consciously discriminate, an algorithm that yields statistically significant worse outcomes for protected classes can trigger liability under disparate impact theory.
- Regulatory Guidance: The FDA’s proposed “Algorithmic Transparency” framework suggests that manufacturers must provide evidence of bias mitigation testing before market clearance.
- Insurance Implications: Professional liability insurers are starting to require evidence of bias audits as part of coverage underwriting.
Mitigation strategies include conducting regular bias audits, diversifying training datasets, and establishing a “human‑in‑the‑loop” safeguard where clinicians review AI‑generated recommendations, especially for high‑risk decisions.
Deepfake Threats in Telemedicine Imaging
While deepfake technology is often discussed in the context of political misinformation, its infiltration into medical imaging is a growing concern. Imagine a patient sending a manipulated MRI scan that appears to show a tumor, prompting unnecessary invasive procedures. The deepfake disruption in synthetic media has already led to legal battles in other industries, and the same trajectory is inevitable in health care.
Legal safeguards you can implement:
- Verification Protocols: Use digital watermarking and blockchain‑based provenance tracking for all imaging uploads.
- Consent and Disclosure: Clearly inform patients that any manipulation of medical images is illegal and can result in criminal prosecution.
- Forensic Review: Partner with radiology groups that employ AI‑based deepfake detection tools as part of the standard intake process.
By integrating technical safeguards with clear policy statements, you create a deterrent that protects both patients and providers from the fallout of fabricated medical evidence.
Cross‑Border Telehealth: International Law and the “Export” of Care
Many U.S. providers are tempted to expand into neighboring Canada, the Caribbean, or even Europe, attracted by the prospect of a broader patient base. However, every country has its own licensing regime, and some treat the provision of remote care as an “export” of medical services, subjecting providers to foreign regulatory approvals.
Considerations include:
- Foreign Medical Licensure: The United Kingdom, for example, requires a “temporary registration” for overseas clinicians providing teleconsultations.
- Data Transfer Restrictions: The EU’s GDPR imposes strict rules on transferring personal health data outside the European Economic Area. Even a brief video call can be deemed a data transfer.
- Reimbursement Policies: Many foreign insurers either do not cover foreign providers or require a local partner to submit claims.
If you’re eyeing an international rollout, start by consulting local counsel in each target jurisdiction, and consider establishing a joint venture with a domestic health entity to navigate licensing and reimbursement hurdles.
Telemedicine and the Rise of “Virtual” Malpractice Insurance
Traditional malpractice policies often exclude “telehealth” or treat it as a separate line of coverage. As the industry matures, insurers are carving out bespoke policies that address the unique exposures of remote care.
Key policy features to watch for:
- Geographic Scope: Does the policy cover all states where you hold a license, or only the state of your primary practice?
- Technology Errors: Coverage for failures of the telehealth platform itself—such as dropped calls, software glitches, or data breaches.
- AI‑Related Claims: Some new policies explicitly include “AI‑driven diagnostic errors” as a covered peril.
When negotiating a policy, ask your broker to provide a “scenario analysis” that maps out potential claim triggers—e.g., a misdiagnosis due to a faulty AI recommendation or a breach caused by a third‑party video vendor. This proactive approach ensures you’re not caught off guard by an unexpected exclusion.
Best‑Practice Checklist for Scaling Telemedicine Legally
To wrap up, here’s a concise, actionable checklist you can run through before expanding your virtual practice:
- Licensure Mapping: Identify every state (and country) you intend to serve. Verify IMLC eligibility, temporary telehealth provisions, or full licensure requirements.
- Privacy Compliance Audit: Align HIPAA policies with state privacy statutes. Implement explicit consent flows and verify data residency capabilities.
- AI Governance: Document AI usage, secure IP rights, and establish explainability standards to mitigate liability.
- Bias Mitigation: Conduct routine bias audits, maintain diverse training datasets, and embed human oversight for high‑risk decisions.
- Deepfake Safeguards: Deploy watermarking, provenance tracking, and forensic review for all patient‑uploaded media.
- International Compliance: Obtain foreign licensure where necessary, respect cross‑border data transfer rules, and partner with local entities for reimbursement.
- Insurance Review: Ensure your malpractice coverage expressly includes telehealth, technology errors, and AI‑related claims.
Telemedicine’s promise is undeniable, but its legal terrain is complex. By taking a systematic, forward‑looking approach, you can harness the power of virtual care while staying firmly on the right side of the law.
Kris M. Chen is a dedicated legal paralegal based in Texas, specializing in delivering comprehensive case management and litigation support. Known for a meticulous approach to legal research and document preparation, Kris plays a vital role in navigating complex legal workflows and ensuring seamless trial preparation.
Related Posts
The New Frontier of Medical Law: Navigating AI, Telehealth, and Data Privacy
A deep dive into how AI-driven diagnostics, the rapid rise of telehealth, and the explosion of weara... Read More
Telemedicine Liability in the Age of AI: A Fresh Legal Playbook
A deep dive into the unique malpractice, licensing, and data‑security risks of AI‑powered telehe... Read More
The Hidden Legal Minefield of Telehealth: What Providers Must Know
Telehealth’s rapid growth has outpaced traditional legal safeguards. This article breaks down the ... Read More
Top Posts
Short‑Term Rental Regulations: Crafting a Balanced Playbook for Hosts and Communities
This article dissects the complex web of short‑term rental laws, offering hosts a clear roadmap that covers permits, insurance, data privacy, community relati...Read More
Right to Disconnect: New Labour Laws Safeguarding Remote Workers
A deep dive into the rise of “right‑to‑disconnect” legislation, its legal foundations, and practical steps employers can take to respect remote workersâ...Read More
When Algorithms Audit Employees: Navigating Labour Law in the Age of AI Performance Metrics
AI-powered performance platforms are reshaping workplace evaluations, raising fresh legal challenges around fairness, employee privacy, and algorithmic transpar...Read More
Untangling SaaS Nexus: Why Subscription Models Are Redrawing State Tax Maps
SaaS founders often underestimate the tax impact of subscription models. This guide breaks down economic nexus, multi‑state automation, remote‑work tax impl...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!