The Hidden Legal Risks of Robotic Surgery
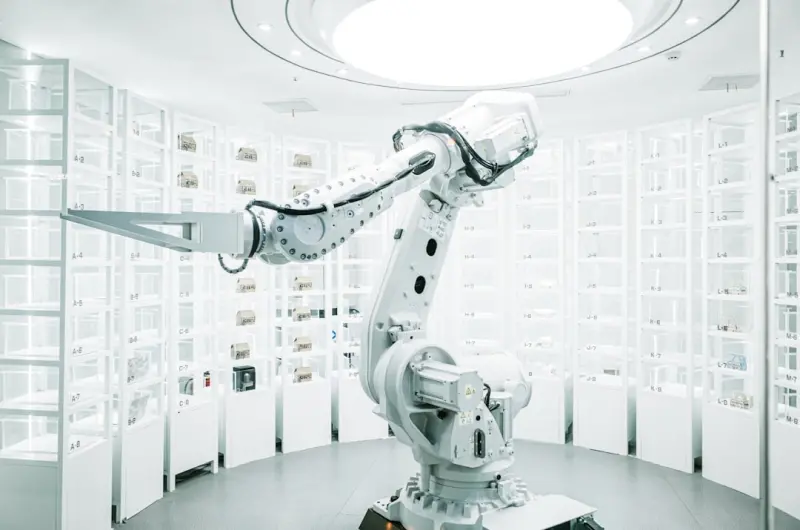
When I first stepped into an operating room equipped with a da‑Vinci console, the blend of precision engineering and human skill felt like science fiction turned tangible. The robot’s arms glided with a steadiness no human hand could match, and the surgeon’s eyes, magnified on a 3‑D screen, guided every incision. Yet, as exhilarating as the technology is, it also raises a cascade of legal questions that most practitioners, administrators, and even insurers are still scrambling to answer.
Why Robotic Surgery Isn’t Just a Technical Upgrade
At its core, robotic surgery is a partnership: the surgeon provides intent, the machine executes with millimetric accuracy. This partnership rewrites the traditional liability framework that has governed surgery for centuries. In the classic malpractice model, the surgeon is the sole actor; the “reasonable physician” standard is applied to his or her actions. Insert a robot, and the calculus becomes murkier. Who is the “reasonable actor” when a robotic arm—guided by software updates, sensor data, and AI‑driven assistance—makes an unexpected movement?
Recent court decisions in other high‑tech arenas hint at how judges might grapple with these dilemmas. For instance, the deepfake disruption cases are forcing courts to distinguish between human intent and algorithmic output. The same analytical lens is now being applied to medical devices that learn from each procedure they perform.
Three Pillars of Liability in Autonomous Surgical Systems
To make sense of the emerging risk landscape, I break it down into three interlocking pillars: device manufacturer responsibility, surgeon duty of care, and institutional oversight.
- Device Manufacturer Responsibility – Manufacturers must prove that their hardware and software meet stringent safety standards. The FDA’s pre‑market approval (PMA) process is only the first hurdle; post‑market surveillance, software patching, and cybersecurity all fall under the manufacturer’s umbrella.
- Surgeon Duty of Care – Even with a robot at the helm, the surgeon retains ultimate control. Courts are likely to continue applying the “reasonable surgeon” test, but they will also evaluate the surgeon’s familiarity with the robot’s interface, training records, and adherence to manufacturer guidelines.
- Institutional Oversight – Hospitals and outpatient centers must implement robust credentialing, maintain logs of software versions, and ensure that any “learning” algorithms are validated before clinical use.
The Software Update Conundrum
Software updates are a double‑edged sword. On one hand, they can patch vulnerabilities, improve performance, and introduce new surgical capabilities. On the other, they can inadvertently introduce bugs that alter the robot’s behavior in subtle ways. Imagine a scenario where a routine patch adds a new collision‑avoidance algorithm, but the calibration data for a specific instrument is off, causing the robot to exert excessive force on tissue.
In the automotive world, the legal challenges of over‑the‑air updates are already a hot topic. Those precedents are bleeding into the medical sphere, with regulators demanding traceability of every code change and clear documentation of who approved the update. Failure to maintain this chain of custody could be construed as negligence, opening manufacturers to product liability claims.
Cybersecurity: The Silent Threat
Robotic systems are networked devices. They communicate with hospital EMRs, imaging suites, and sometimes even cloud‑based analytics platforms. A breach could allow an attacker to hijack the robot’s controls, inject malicious code, or corrupt data logs that are critical for post‑operative analysis.
Legal scholars are already debating whether a cyber‑attack that results in patient harm should be treated as a traditional malpractice claim, a product liability suit, or a new category of “cyber‑medical” negligence. The answer may hinge on the concept of “reasonable cybersecurity practices,” a standard that is still being defined across industries.
Informed Consent in the Age of Autonomy
Informed consent has always required that patients understand the risks, benefits, and alternatives to a proposed treatment. With robotic surgery, the consent conversation must now also cover the technology itself: the role of AI, the possibility of software glitches, and the manufacturer’s liability limits.
Recent legal commentary on genetic data consent underscores the importance of clear, transparent disclosures. Similarly, surgeons must explain that while the robot can enhance precision, it is not infallible. Failure to disclose these nuances could be grounds for a claim of inadequate consent.
Cross‑Border Considerations: Tele‑Robotics
Tele‑robotic surgery—where a surgeon operates a robot located in a different state or even country—adds another layer of complexity. Jurisdictional questions arise: Which state’s malpractice laws apply? Does the surgeon’s licensure cover remote operations? And what about the device manufacturer’s liability when the robot is shipped across borders?
Our industry’s recent cross‑state telemedicine strategies offer a useful template. The same principles of licensure verification, data privacy compliance, and clear contractual agreements between the surgeon, the host facility, and the patient must be replicated in tele‑robotics.
Insurance Landscape: Who Pays the Bill?
Malpractice insurers are still calibrating their risk models for robotic procedures. Some policies now include specific “robotic surgery” endorsements, which adjust premiums based on the type of device, the surgeon’s experience, and the institution’s safety protocols.
Insurers are also demanding that hospitals maintain detailed logs of every robotic case, including software versions, surgeon credentials, and intra‑operative events. These logs become critical evidence in any subsequent litigation, and their absence can trigger denial of coverage.
Best Practices for Mitigating Legal Exposure
Below are actionable steps that stakeholders can adopt today to shore up their defenses against emerging liability risks:
- Comprehensive Training Programs – Require surgeons and OR staff to complete certified training that is refreshed annually. Document competency assessments and tie them to credentialing.
- Software Version Control – Maintain a centralized repository of all device software versions, patches, and associated approval signatures. Implement a rollback procedure for any problematic update.
- Cybersecurity Audits – Conduct regular penetration testing and risk assessments on all robotic platforms. Adopt industry standards such as the NIST Cybersecurity Framework.
- Enhanced Informed Consent Forms – Include explicit language about the robot’s role, potential software-related risks, and the manufacturer’s liability scope.
- Robust Data Logging – Use immutable logging systems to capture every command sent to the robot, sensor readouts, and any deviations from expected performance.
- Clear Contracts for Tele‑Robotics – Draft agreements that delineate jurisdiction, licensure requirements, data protection obligations, and indemnification clauses.
- Insurance Alignment – Work closely with carriers to ensure policies cover both surgeon and device manufacturer liabilities, and that they reflect the latest risk assessments.
Looking Ahead: The Regulatory Horizon
The FDA is moving toward a more proactive approach, introducing the Pre‑certification Program for software as a medical device (SaMD). This could streamline approvals for incremental software updates but also imposes stricter post‑market surveillance obligations. Expect to see more “real‑world evidence” requirements, where hospitals must submit performance data back to manufacturers and regulators.
Internationally, the European Union’s Medical Device Regulation (MDR) already mandates a higher level of traceability and post‑market vigilance. As manufacturers aim for global market access, they will need harmonized compliance frameworks that satisfy both FDA and MDR standards—a challenge that will inevitably filter down to legal risk management.
Conclusion: Embracing Innovation While Guarding Against Risk
Robotic surgery promises to reduce human error, improve outcomes, and expand the reach of minimally invasive procedures. Yet, the very technology that offers these benefits also rewrites the rules of liability, consent, and regulatory compliance. By understanding the three pillars of responsibility, staying ahead of software and cybersecurity developments, and adopting rigorous best practices, surgeons, hospitals, and manufacturers can navigate this brave new world with confidence.
The stakes are high, but so is the potential for transformative patient care. The legal community must evolve in tandem, crafting doctrines that recognize the hybrid nature of human‑machine collaboration while preserving the core principles of patient safety and accountability.
Liam James Professor with a PHD. & content creator with a passion for sparking curiosity and sharing knowledge. Driven by the joy of learning and storytelling, I bring ideas to life in every project. Always exploring, always teaching.
Related Posts
Trending Medical Law Insights for 2024: Margaret Strawbridge’s Perspective
Margaret Strawbridge breaks down the hottest medical law trends of 2024, highlighting telemedicine, ... Read More
Beyond the Stethoscope: Legal Challenges of Wearable Health Tech
Wearable health devices turn patients into continuous data sources, raising new legal questions abou... Read More
Navigating the Legal Labyrinth of Modern Telemedicine
A deep dive into telemedicine’s legal challenges—licensing, privacy, AI, and more—offering pra... Read More
Top Posts
Data Monetization Meets Tax: Uncovering Hidden Liabilities in the Age of Insight‑Driven Revenue
A deep dive into the tax implications of data‑driven business models, covering classification, jurisdictional nexus, revenue recognition, and hidden credits t...Read More
Turning a Personal Injury Setback into a Strategic Victory
Discover how early documentation, smart witness handling, and awareness of modern tech can turn a personal injury setback into a winning legal strategy....Read More
Beyond the Bed: Unpacking the Legal Labyrinth of Short‑Term Rentals
A comprehensive guide to the legal challenges of short‑term rentals, covering permits, zoning, HOA rules, insurance, taxes, guest safety, data privacy, and fu...Read More
Deepfake Dilemmas: How the Law is Racing to Catch Synthetic Media
Deepfake technology is reshaping truth. This post untangles the legal maze, highlighting current laws, state battles, and future reforms while offering actionab...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!